
 uBlock Origin
一款高效的网络请求过滤工具,占用极低的内存和 CPU。
Firefox

Eval Villain EN
bemodtwz · Firefox
Hook native JavaScript functions before page load to see how a website uses them. Narrow down output based on the appearance of URL and session artifacts, user configured strings/regex, blacklists and more.
3.7/5
3 人评分
179用户
v2.11当前版本
权限提示
该扩展申请访问所有网站(
<all_urls>),意味着它可以读取你在任意站点的页面内容,包括已登录的页面。这是许多扩展正常工作的必要条件,但也值得你确认来源可信。
截图
简介
Eval Villain hooks JavaScript sinks and monitors input for the presence of strings found in sources. There is no race condition as Eval Villain will hook sinks before they can be used. Sinks will be hooked in all frames and pages unless a target URL pattern is configured.
The default configuration will hook common DOM XSS sinks but Eval Villain can be configured to hook any function. Go to the configuration page and click the icon -> configure to see examples.
When a sink is called, Eval Villain goes through a list of sources and tests input to that function for any occurrence of the sources. Sources include user defined strings or regex (referred to as needles), URL parameters, URL fragments (aka hash), local storage, window name and the user cookie. There is also a blacklist feature to remove commonly occurring false positives. Each of these features can be individually enabled or disabled in the popup menu. When changes are made, the page will need to be refreshed for changes to take effect.
These features make Eval Villain well suited to find DOM XSS, but also to answer other questions about how a web page is functioning. Hooking eval() and dumping input can bypass common obfuscation techniques and even find malware. Hooking decodeURI() with the URL parameter source enabled will give a stack trace that often contains the website's URL parser. Instrumenting the parser can then expose hidden URL parameters. Hooking addEventListener() with the needle "message" will dump the source code and location of post message handlers. Eval Villain allows a lot of configuration options to allow for creative solutions.
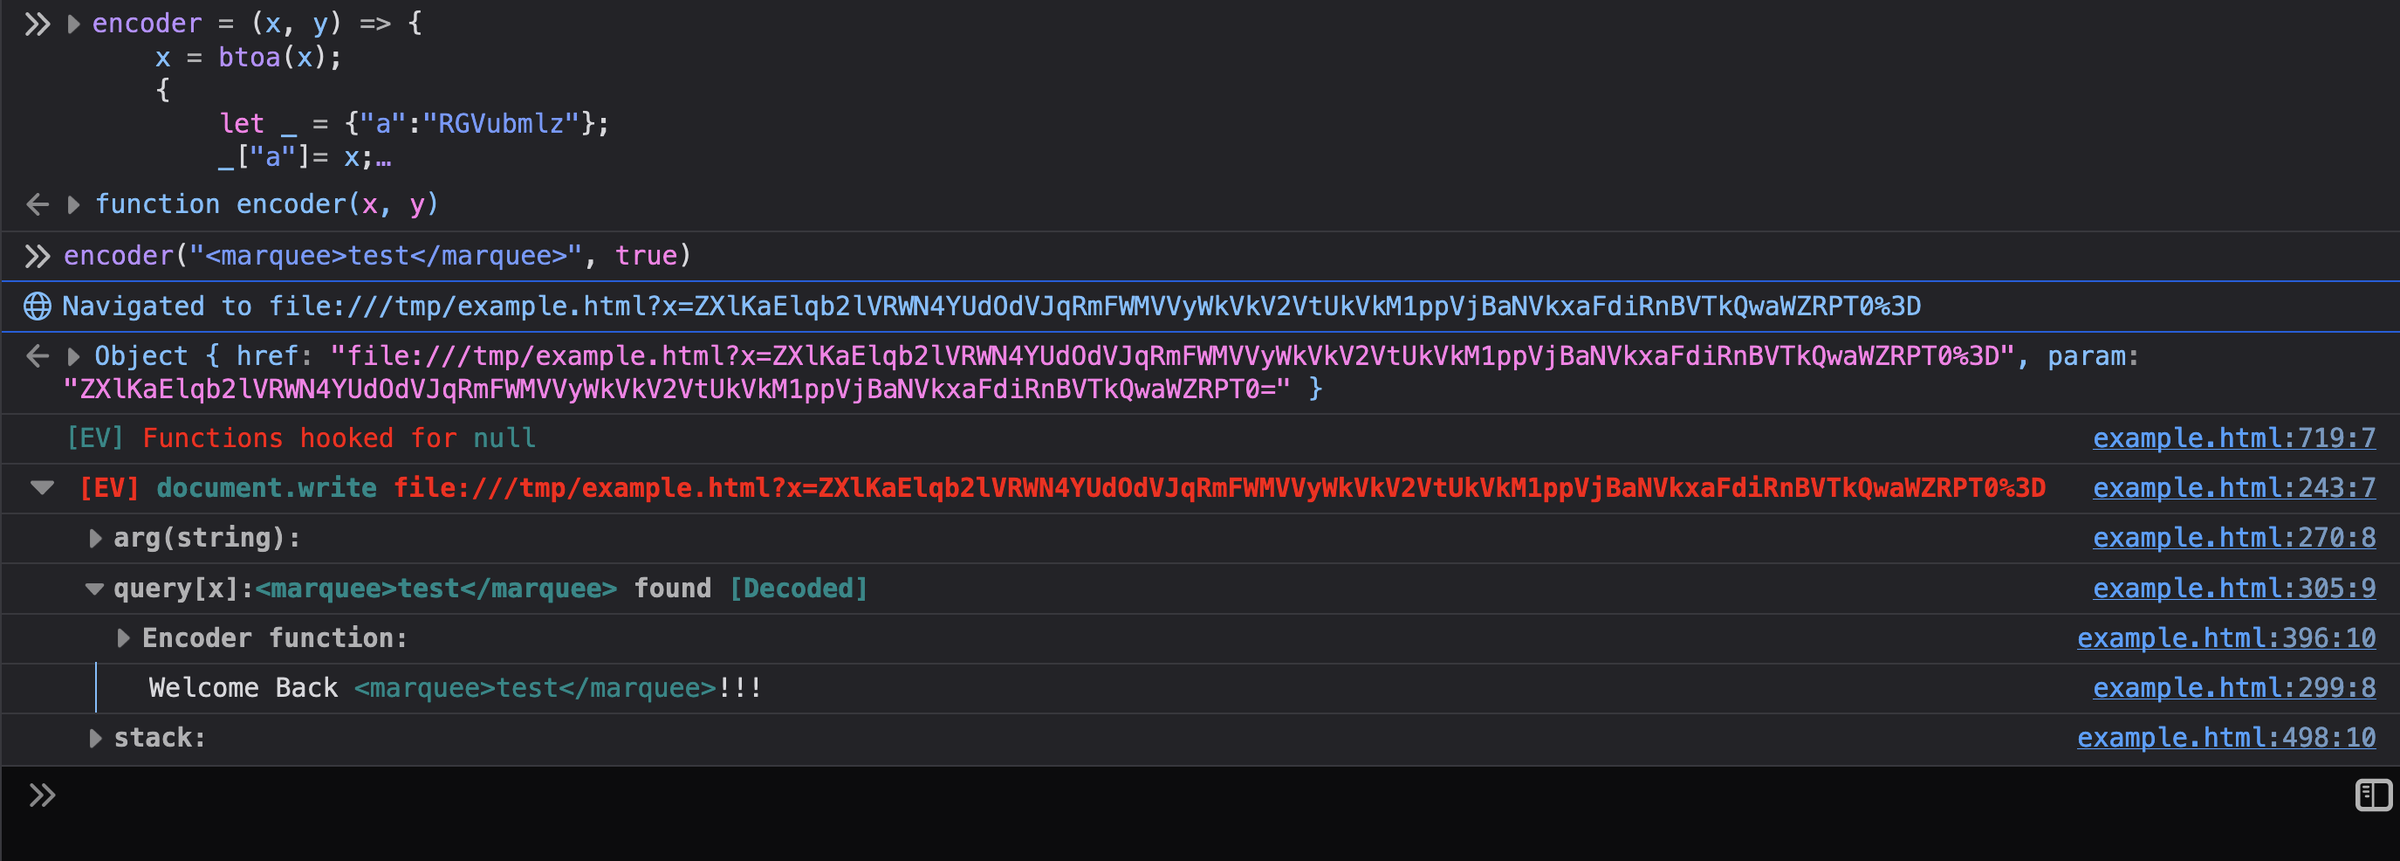
Eval Villain will also attempt to recursively decode sources. For example, ad networks often build iframes with encoded HTML hidden in the window name. Eval Villain can detect this behavior and provide both the sink where the HTML lands and an encoder function to encode arbitrary HTML into the frame.
Support for this version provided by Doyensec Research https://doyensec.com/research.html
Eval Villain 是做什么的
Eval Villain 是一款面向 Firefox 的开发者工具类扩展,主要用来调试页面、查看样式与请求、测试接口、辅助前端开发。官方对它的介绍是:Hook native JavaScript functions before page load to see how a website uses them. Narrow down output based on the appearance of URL and session artifacts, user configured strings/regex, blacklists and more.在Firefox 附加组件商店(AMO)上,它当前版本 2.11,评分 3.67(3 人评价),约 179 名用户。
适合什么人用
从功能定位看,Eval Villain 更适合前端工程师、测试与需要经常查看页面结构的用户。如果你平时只是偶尔遇到相关需求,用浏览器自带功能也能凑合;但如果这件事每天都发生,装一个专门处理它的扩展通常比手动操作省事得多。需要注意的是它作用于所有网站,装上后建议先观察一两天,确认不影响常用站点的正常使用。
怎么安装 Eval Villain
- 打开Firefox 附加组件商店(AMO)上的官方页面;
- 点「添加到浏览器」并确认权限提示;
- 装好后在扩展列表里固定图标,方便随时开关。
本站只做索引与介绍,安装包来自官方商店。如果商店页面提示当前地区不可用,说明该扩展未在你所在区域上架。
常见问题
Eval Villain 是免费的吗?
Eval Villain 在Firefox 附加组件商店(AMO)免费提供下载。它是浏览器扩展,装上就能直接用,不需要注册账号。
Eval Villain 安全吗?
它只申请了 0 项权限,范围比较克制,没有申请「读取所有网站数据」这种大权限。
Eval Villain 支持哪些浏览器?
当前收录的版本来自Firefox 附加组件商店(AMO),适用于 Firefox。同一个扩展在其他商店可能有对应版本,但功能与版本号不一定相同。
怎么卸载 Eval Villain?
在扩展管理页找到 Eval Villain,点移除即可。它在本地保存的设置会一起清掉,不会残留数据。
权限清单 来自 manifest.json 原文
站点访问 1
<all_urls>
接口权限 1
storage
标签 点标签看同类扩展
uBlock Origin
一款高效的网络请求过滤工具,占用极低的内存和 CPU。
Firefox
 AdGuard AdBlocker
AdGuard 广告拦截器可有效的拦截所有网页上的所有类型的…
Firefox
 AdBlocker Ultimate
Completely remove ALL ads. No …
Firefox
 Bitwarden – 免费密码管理器
安全免费的跨平台密码管理器
Firefox
 Malwarebytes Browser Guard
Fast and safe browsing that pr…
Firefox
 Firefox Multi-Account Containers
Firefox Multi-Account Containe…
Firefox
 LastPass Password Manager
LastPass是一款让您的上网浏览更便捷更安全的免费在线密…
Firefox
 1Password: Password Manager
The best way to experience 1Pa…
Firefox